Issue
- Prevent the loss of internet connectivity on client computers due to firewall settings when deploying ESET Endpoint Security
- Add the IP range/subnets to the trusted zone before deploying ESET Endpoint Security
- Edit or disable Firewall rules in ESET PROTECT or ESET PROTECT On-Prem
Solution
Add the IP range/subnets to the trusted zone before deploying ESET Endpoint Security
To resolve your RDP/ping issue, configure the trusted zone with the IPv4 and Remote IP addresses, ranges, masks, and subnets, including any VPN networks and all subnets inside your network.
-
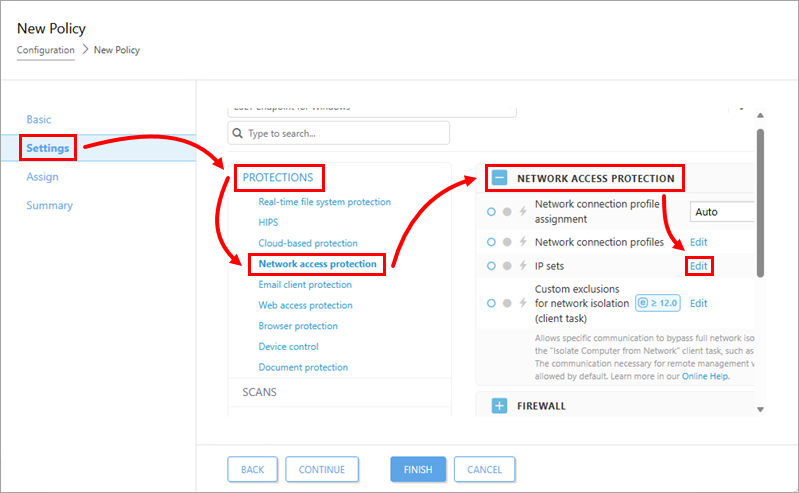
In the Settings section, click Protections → Network access protection, expand Network access protection and click Edit next to IP sets.
-
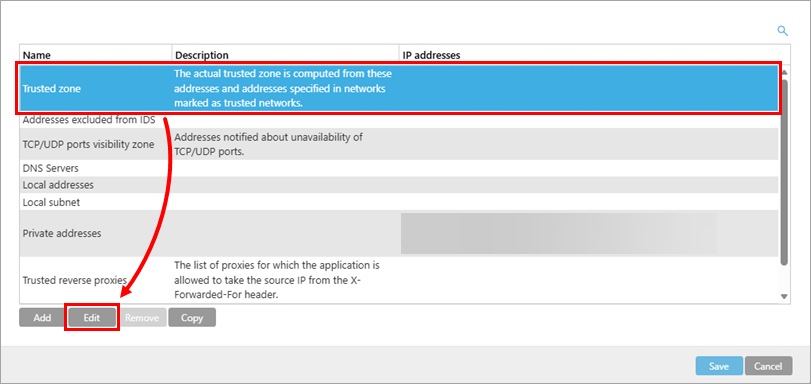
Select Trusted zone and click Edit.
-
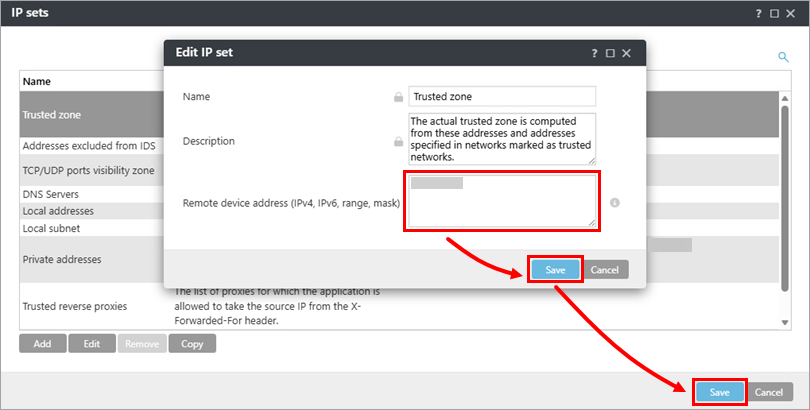
In the Remote device address (IPv4, IPv6, range, mask) field, add your IPv4 and Remote IP addresses, ranges, masks, and subnets, including any VPN networks and all subnets inside your network. Click Save → Save → Finish.
-
When the system checks into ESET PROTECT or ESET PROTECT On-Prem with the new settings, you can deploy ESET Endpoint Security to your network.
Edit or disable Firewall rules in ESET PROTECT or ESET PROTECT On-Prem
-
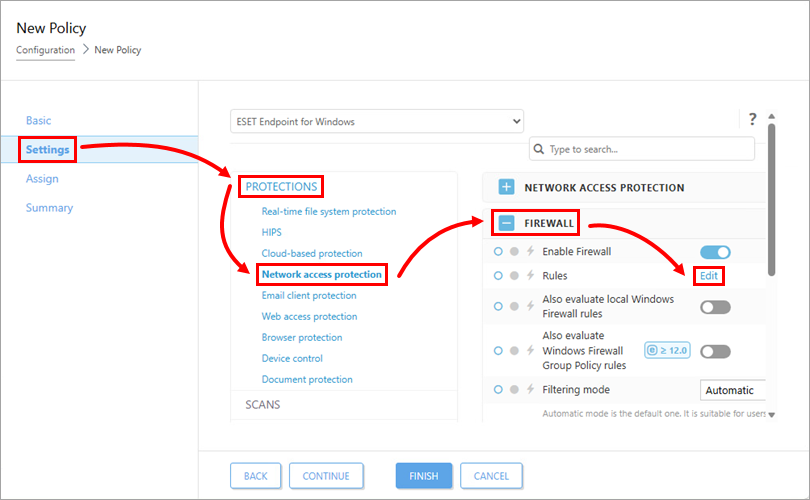
In the Settings section, click Protections → Network access protection, expand Firewall, and click Edit next to Rules.
-
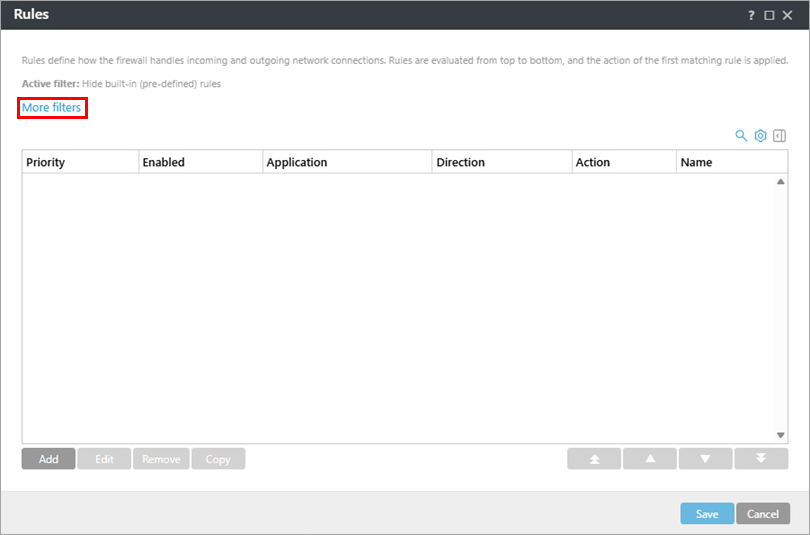
Click More filters.
-
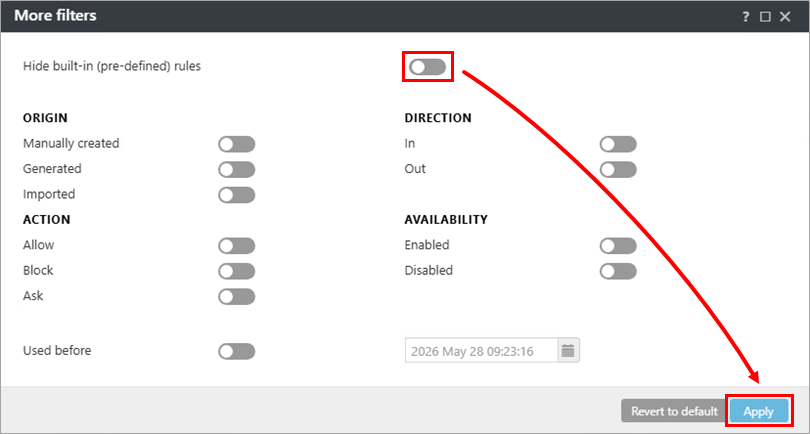
Select the check box next to Hide built-in (pre-defined) rules to turn it off, and click Apply.
-
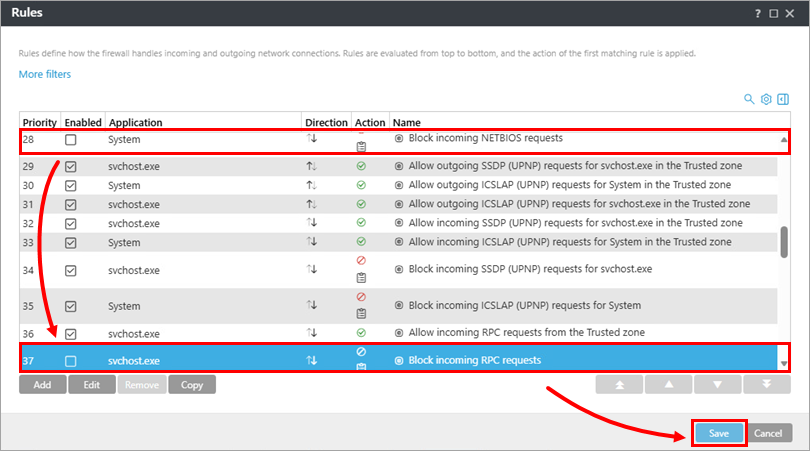
Deselect the check boxes next to Block incoming NETBIOS requests and Block incoming RPC requests, and click Save → Finish.
-
When the system checks into ESET PROTECT or ESET PROTECT On-Prem with the new settings, you can deploy ESET Endpoint Security to your network.


